Secure application development, identity and access management, DevSecOps and penetration testing. We find the gaps in your software and accounts, fix them, and check that the fix holds.
Build it safe, control who gets in, check every release, and test it the way an attacker would. Take one service or all four. Most clients start with an audit.
A qualified tester tries to break in, with your written permission, and shows what could be reached. SOC monitoring and incident response cover what happens after.
Burp Suite
OWASP ZAP
Wazuh
Elastic
CrowdStrike
Illustrative examples. The logos are tools we work with, not partnerships.
Here one second, gone the next
Customer list
Card payments
Passwords
Invoices
Gone before your coffee got cold.
Back where it belongs, and locked this time. That is the job.
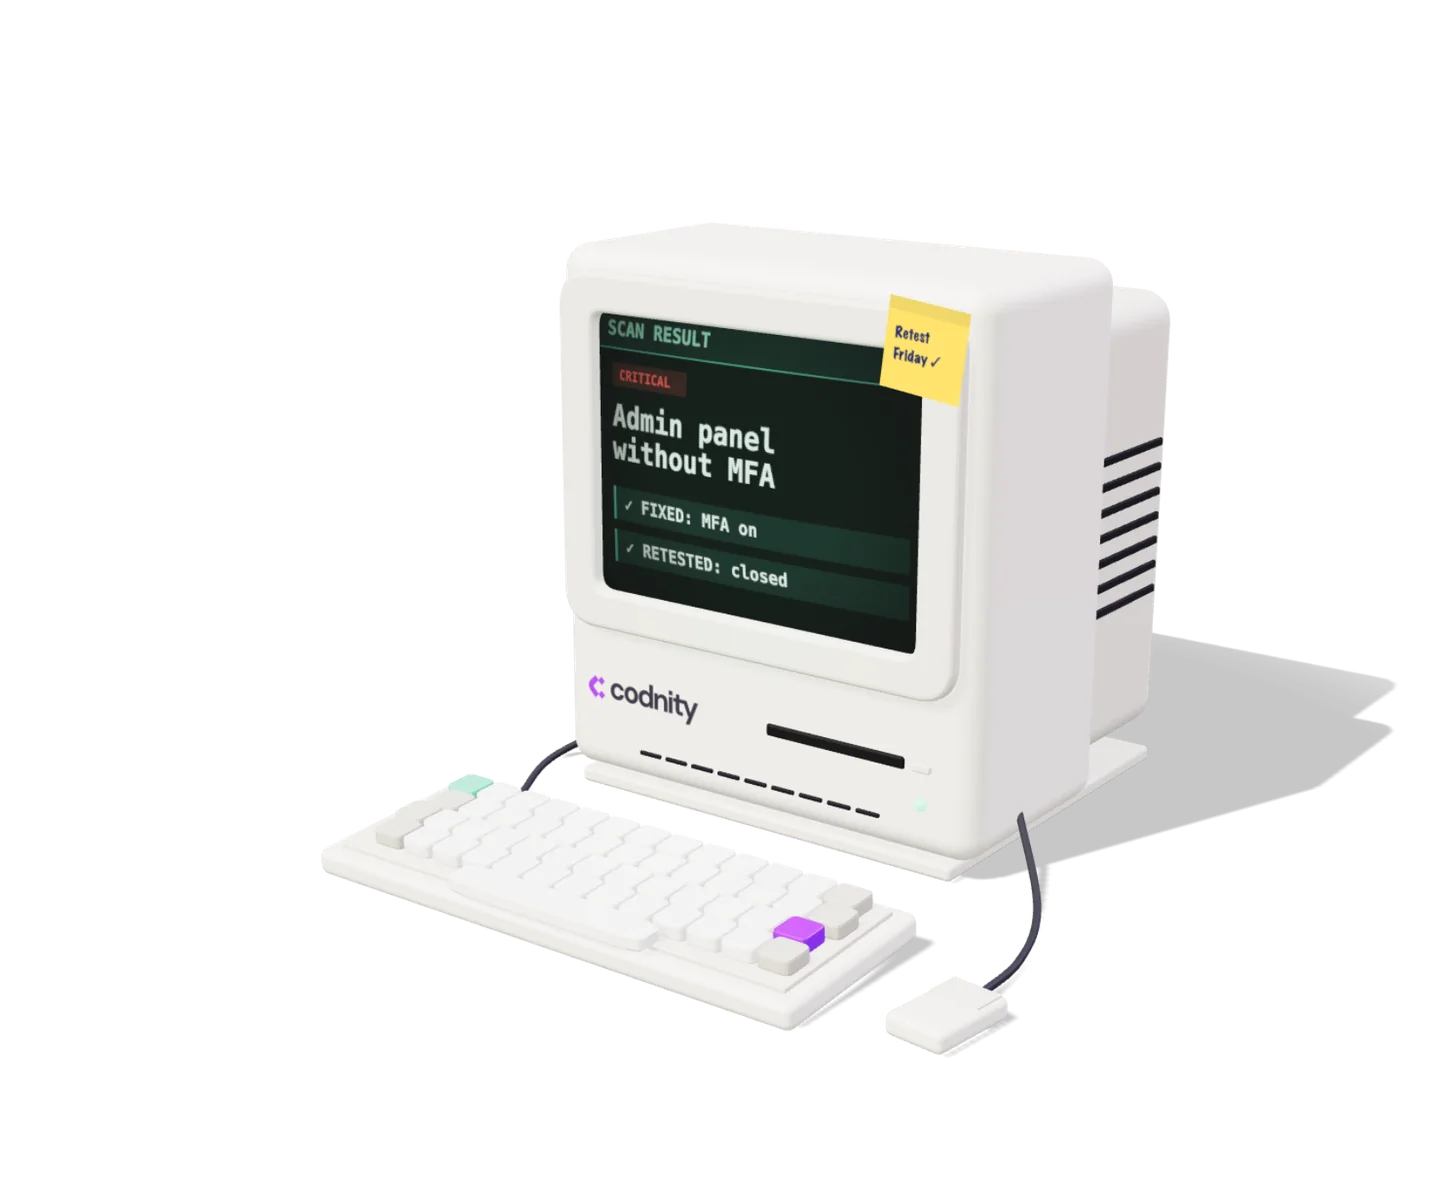
It usually starts small: a reused password, an admin without MFA, a test server nobody remembers. We find those first.
Psst. Click him.
How a cybersecurity audit works
Most clients start here. We check the basics behind most incidents, rank what we find and help you close it.
Check 1 to 2 weeksAccounts and MFA, apps and APIs, cloud and backups. Every finding comes with evidence and a risk rating.
Fix riskiest firstIn code, access and the release pipeline. We do it, or your team does it with our notes.
RetestEach fix is checked against the original evidence.
Monitor if you want itSOC monitoring, and a penetration test once a year or before a big launch.
Orvela Logistics SIA · Retest
Retest · 13 Oct 2026Against the 2 Sep audit
Audit2 Sep16 open
Retest13 Oct6 open
CriticalHighMediumLow
F-01Admin accounts without MFACriticalFixed, verified
F-02API returns other customers' dataHighFixed, verified
F-03Database password in the pipelineHighFixed, verified
Illustrative example.
NIS2 readiness in Latvia
If Latvia's National Cybersecurity Law applies to you, we map each requirement to your evidence and close the technical gaps. The National Cybersecurity Centre's online test tells you whether it applies.
Short answers to what buyers ask before they call. Ask Cody for anything else.
What cybersecurity services does Codnity offer?
+
Codnity offers four cybersecurity services: secure application development, identity and access management, DevSecOps implementation, and penetration testing with SOC monitoring and incident response. Most clients start with a cybersecurity audit, which shows which of the four they need first.
What do buyers and investors ask about security in due diligence?
+
Buyers and investors usually ask for a recent penetration test, how access and MFA are managed, how backups are tested and whether there were incidents. A cybersecurity audit before the process gives you the answers and time to fix the gaps.
Is AI a security risk for our company?
+
AI becomes a security risk when staff paste customer data into chatbots or when AI agents get broad access to your systems. We set rules for which tools and data are allowed, give each agent only the access it needs and log what it does.
What is secure application development?
+
Secure application development means security is built into web and mobile apps from the first sprint: API hardening, authentication and an access check on every request, with tests that keep them in place. We follow the OWASP guidance for web apps and APIs.
How should we set up SSO, MFA and passkeys?
+
Put staff apps behind one identity provider with single sign-on, require MFA for everyone and give admins passkeys or security keys. Grant access through roles (RBAC) built from real job tasks, and link joiners and leavers to HR records so access changes the same day.
What is DevSecOps?
+
DevSecOps adds security checks to the way you build and release software. Dependency scanning, secret scanning, tests and a required review run on every change in your CI/CD pipeline, and passwords and keys move into a secrets manager.
What is the difference between vulnerability scanning and penetration testing?
+
Vulnerability scanning uses automated tools to list known weaknesses across many systems. Penetration testing is manual: a qualified tester tries to break in under written authorisation and shows what could actually be reached. Scans run often, penetration tests before a launch or once a year.
Do you provide SOC monitoring and incident response?
+
Yes, SOC monitoring watches your sign-ins, logs and alerts within agreed hours, and incident response helps you contain an incident and find its cause. We agree the coverage and response times in writing, and say upfront if a partner runs part of it.
What is a cybersecurity audit?
+
A cybersecurity audit checks your accounts, apps and APIs, cloud and backups for the gaps behind most incidents, such as admin accounts without MFA or an API that shows too much. You get a ranked list of findings with evidence and a fix for each, and a retest after the fixes.
Does NIS2 apply to our company?
+
NIS2 applies if your company is an essential or important entity under Latvia's National Cybersecurity Law, which depends on your sector and size. The National Cybersecurity Centre's online test gives a first answer, and your legal adviser confirms it.
Can Codnity help with NIS2 readiness?
+
Yes, Codnity helps with the technical side of NIS2 readiness. We map each requirement to the evidence you already have, close the gaps and prepare the evidence. It does not replace legal advice or a certification.
How much do cybersecurity services cost?
+
The cost of cybersecurity services depends on how many systems are in scope and how deep the work goes. We agree the scope in a short call and give you a fixed price before any work starts.
Tell us what worries you
What you run, what changed and any deadline or client requirement. We reply within one working day with what to check first.
Talk to the people doing the work
Jānis leads Cybersecurity & IT and replies within one working day.
Or write directlyhello@codnity.comRiga · London · US East Coast
What comes next
Once the gaps are closed, plan the next step, and connect your systems safely.




 OWASP
 Cloudflare
 Auth0
 Keycloak
 Microsoft Entra ID
 Okta
 Google Workspace
 YubiKey
 Passkeys
 1Password
 GitHub Actions
 GitLab
 Snyk
 SonarQube
 Dependabot
 HashiCorp Vault
 Burp Suite
 OWASP ZAP
 Wazuh
 Elastic
 CrowdStrike